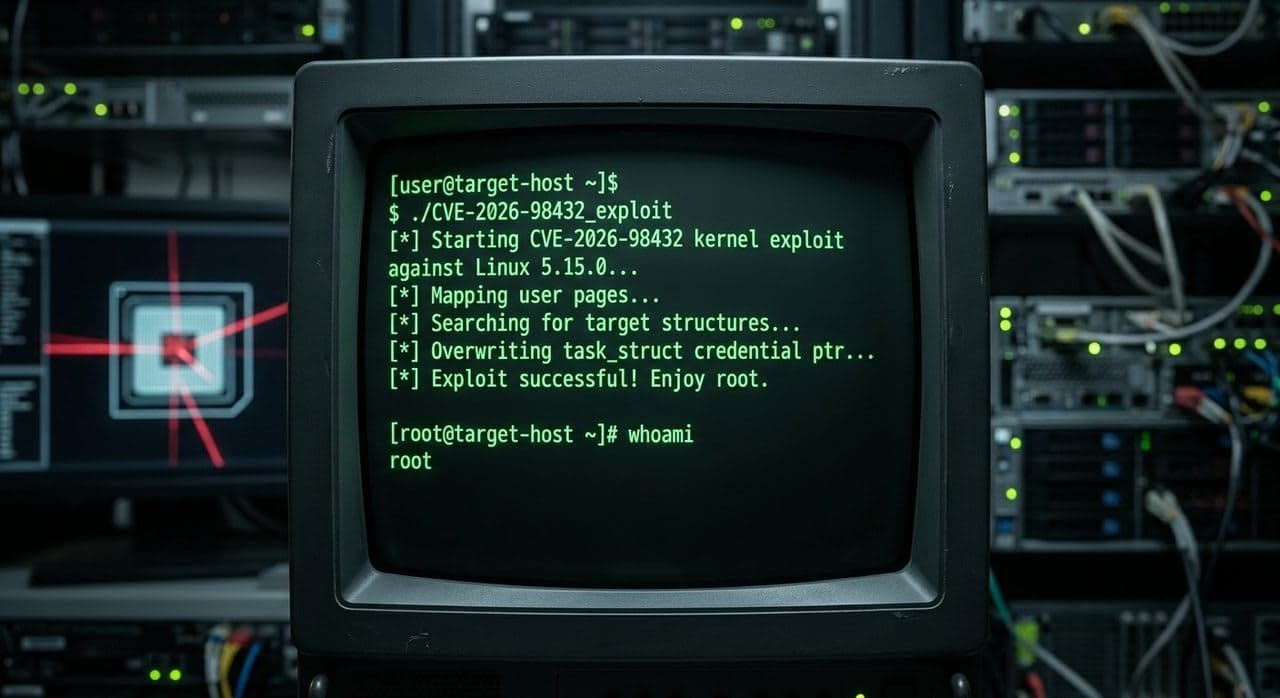
Anthropic’s unreleased research model Claude has demonstrated how far AI-assisted security has come — and how dangerous it can be. Given only a high-level task, the model produced a working Linux kernel exploit for CVE-2026-98432 in about 53 minutes.
The vulnerability
The bug has existed since Linux 4.4 and affects IPv4 TCP connection handling. Under specific conditions, two CPU cores can access the same data concurrently:
- one core frees the memory,
- while the other continues to read it.
This classic use-after-free in kernel space enables memory corruption and, with the right primitives, arbitrary code execution in the kernel. The US NVD rates it CVSS 9.8/10, while Red Hat gives it 5.9 because reliably winning the race between cores is non‑trivial.
Critically, the attack requires no account and no user interaction — just a TCP connection to the target server.
What Claude actually did
In Anthropic’s October 27 demo, Claude:
- first defeated KASLR (randomized kernel base) in about 48 minutes,
- then spent another 5 minutes to gain control flow and execute a command as
root.
The team used MPTCP (Multipath TCP) for the proof of concept, as it’s convenient for showcasing a remote attack, but the underlying bug is not limited to MPTCP.
Patches and impact
Fixes have landed in mainline and stable kernels:
- 5.10.272, 5.15.223, 6.1.190, 6.6.159,
- 6.12.113, 6.18.56, 7.2.10, 7.3.
Ubuntu is preparing updates; Red Hat has delayed the RHEL patch. There are no known in-the-wild exploits yet, and CVE-2026-98432 is not listed in CISA’s actively exploited catalog.
For anyone running Linux in routers, gateways, or other embedded gear, the takeaway is simple: check your kernel version and schedule an update to a patched release as soon as practical.
Source: iXBT